XZ Outbreak CVE-2024-3094
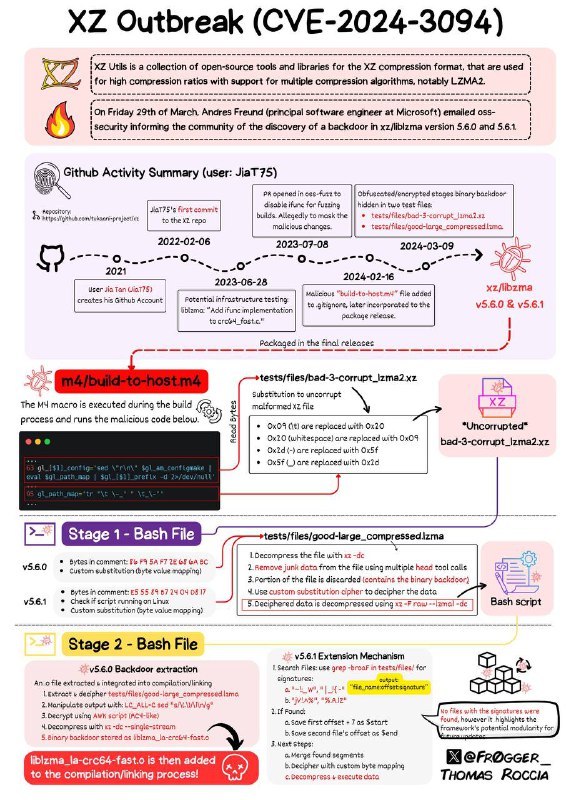
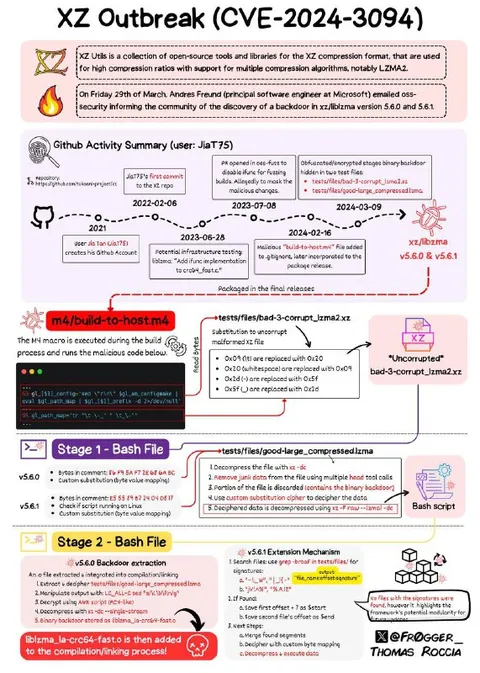
XZ Outbreak (CVE-2024-3094) XZ Utils is a collection of open-source tools and libraries for the XZ compression format, that are used for high compression ratios with support for multiple compression algorithms, notably LZMA2. On Friday 29th of March, Andres Freund (principal software engineer at Microsoft) emailed oss-security informing the community of the discovery of a backdoor in xz/liblzma version 5.6.0 and 5.6.1 Github Activity Summary (user: JiaT75) repository xz:liblzma JiaT75’s first commit to the xz repo 2022-06-06 PK opened in oss-fuzz to disable afl++ fuzzing builds. Allegedly to mask the malicious changes. 2023-07-08 Obfuscated/encrypted staging binary hidden in two test files: tests/files/bad-5-corrupt_lzma2.xz tests/files/good-large_compressed.lzma 2023-09-04 2021 User Jia Tan (JiaT75) creates his Github account 2023-06-28 Potential infrastructure testing by JiaTan. “Add func in implementation to credit_fasta.” 2024-02-16 Malicious “build-to-host” file added to xz/liblzma, later incorporated to the package release. 2024-02-29 xz/liblzma v5.6.0 & v5.6.1 Packaged in the final release m4/build-to-host.m4 The M4 macro is executed during the build process and runs the malicious code below. Bad Bytes tests/files/bad-3-corrupt_lzma2.xz substitution to corrupt malformed xz file 0x09 (0x1) are replaced with 0x20 0x20 (whitespace) are replaced with 0x09 0x2d (-) are replaced with 0x5f 0x5f (_) are replaced with 0x2d “Uncorrupted” bad-3-corrupt_lzma2.xz Stage 1 - Bash File v5.6.0 Bytes in comment: FB F9 A7 2E 6A 0A BC Custom substitution (byte value mapping) v5.6.1 Bytes in comment: E5 55 9F 67 24 0D 17 check if script running on Linux Custom substitution (byte value mapping) tests/files/good-large_compressed.lzma 1. Decompress the file with xz -dc 2. Remove . from the file using multiple head tools 3. Portion of the file is discarded (contains the binary backdoor) 4. Use custom substitution cipher to decipher the data 5. Decrypted data is decompressed using xz -F raw --lzma2 -dc Bash script Stage 2 - Bash File v5.6.0 Backdoor extraction An .lzma file extracted and integrated into compilation/linking 1. Extract + decipher tests/files/good-large_compressed.lzma 2. Manipulate output with _ALL_C_ sed "tr\n..." 3. Decrypt using Aml script (pick-like) 4. Decompress with xz -dc --single-stream 5. Binary backdoor stored in lzma_c… 5.6.1 Extension Mechanism 1. Functionals file: grep --for each in tests/files/for signatures: output "file_name%signature" 2. If found: A. Save first offset + 7 as Start B. Save second file offset as End 3. Next steps: A. Merge found segments B. Decipher with custom byte mapping C. Decompress + execute data lzma_c−crc64-fast.o is then added to the compilation/linking process! No files with the signatures were found, however it highlights the framework’s potential modularity @FROGGER_ THOMAS ROCCIA
Это техническая инфографика о бэкдоре XZ Utils CVE-2024-3094. Она показывает цепочку подозрительных коммитов, вредоносные тестовые файлы и двухэтапный механизм Bash-бэкдора, который встраивался в процесс сборки и линковки. Шутка здесь в том, что сложная схема выглядит как расследование тщательно спланированной атаки на цепочку поставок программного обеспечения; такой мем отправляют в обсуждениях Linux, безопасности и open source, когда нужно показать масштаб инцидента. EN: This technical infographic explains the XZ Utils CVE-2024-3094 backdoor. It shows the chain of suspicious commits, malicious test files, and the two-stage Bash backdoor mechanism that was inserted into the build and linking process. The joke is that the elaborate diagram looks like an investigation of a carefully planned software supply-chain attack; people send this meme in Linux, security, and open-source discussions to convey the scale of the incident.
- @gentoomemes / 10274 2024-03-31
- Type
- image
- Size
- 571×800 · 149.2 KiB
- Mood
- тревожный, технический
- Language
- en
- Added