Kernel and Userland Sauce
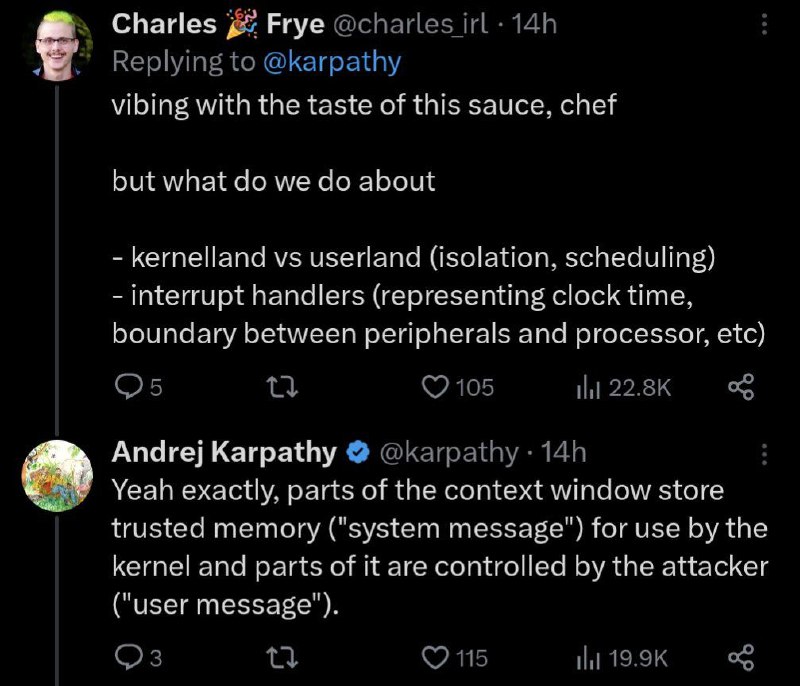
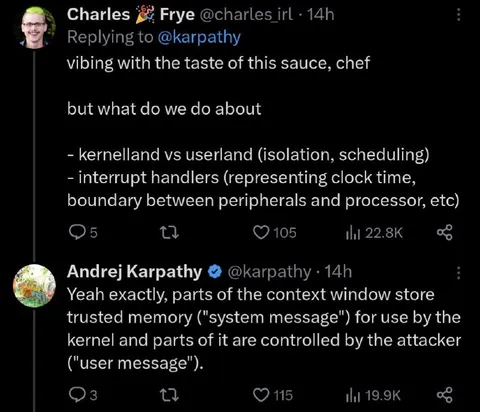
vibing with the taste of this sauce, chef but what do we do about - kernelland vs userland (isolation, scheduling) - interrupt handlers (representing clock time, boundary between peripherals and processor, etc) Yeah exactly, parts of the context window store trusted memory ("system message") for use by the kernel and parts of it are controlled by the attacker ("user message").
A dark-mode social media thread compares the architecture of an AI context window to an operating system, discussing kernel versus userland, interrupt handlers, trusted memory, and attacker-controlled user messages. The joke is that the technical explanation treats prompt injection and message hierarchy like an operating-system security problem, while the opening describes it as tasting a sauce. It is shared as a reaction to clever AI or cybersecurity analogies. EN: A dark-mode social media thread compares the architecture of an AI context window to an operating system, discussing kernel versus userland, interrupt handlers, trusted memory, and attacker-controlled user messages. The joke is that the technical explanation treats prompt injection and message hierarchy like an operating-system security problem, while the opening describes it as tasting a sauce. It is shared as a reaction to clever AI or cybersecurity analogies.
- @gentoomemes / 7285 2023-11-11
- Type
- image
- Size
- 800×686 · 89.5 KiB
- Mood
- technical, absurd
- Language
- en
- Added