Age Verification App Security Disaster
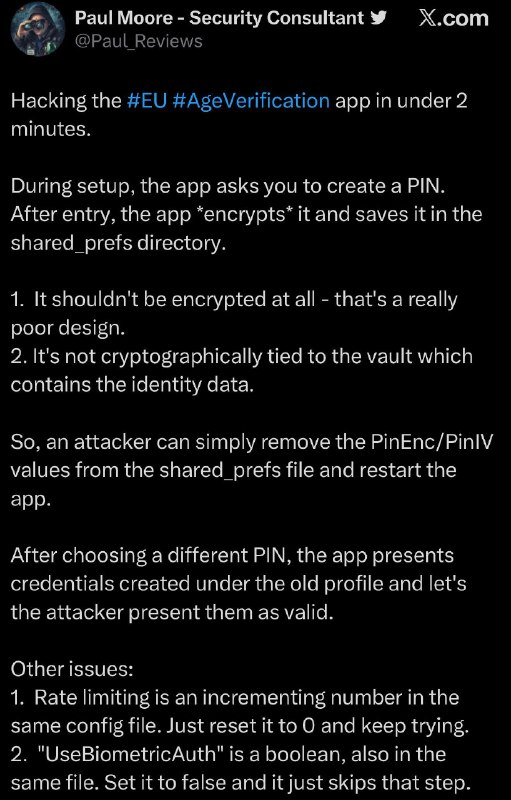
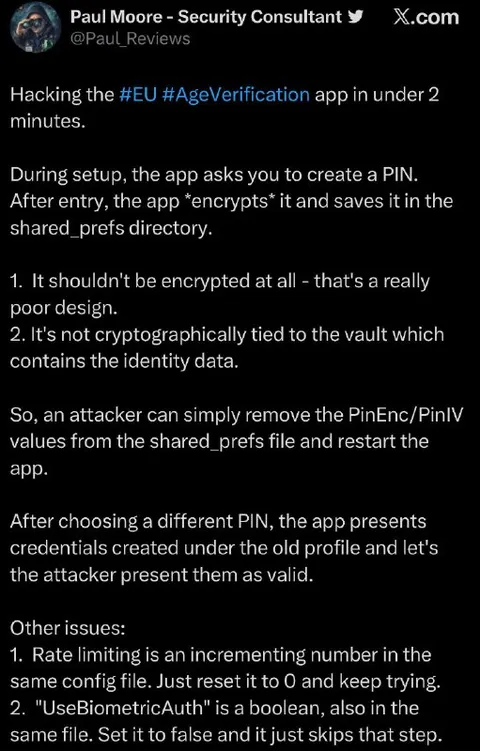
Paul Moore - Security Consultant @Paul_Reviews Hacking the #EU #AgeVerification app in under 2 minutes. During setup, the app asks you to create a PIN. After entry, the app *encrypts* it and saves it in the shared_prefs directory. 1. It shouldn't be encrypted at all - that's a really poor design. 2. It's not cryptographically tied to the vault which contains the identity data. So, an attacker can simply remove the PinEnc/PinIV values from the shared_prefs file and restart the app. After choosing a different PIN, the app presents credentials created under the old profile and let's the attacker present them as valid. Other issues: 1. Rate limiting is an incrementing number in the same config file. Just reset it to 0 and keep trying. 2. "UseBiometricAuth" is a boolean, also in the same file. Set it to false and it just skips that step.
Скриншот поста в X, где автор описывает, как обойти приложение проверки возраста ЕС менее чем за две минуты. Шутка строится на абсурдно слабой реализации безопасности: PIN, лимит попыток и биометрия хранятся в доступном конфигурационном файле, поэтому защиту можно легко сбросить.
social media post / пост в социальной сетиX.com interface / интерфейс X.comprofile avatar / аватар профиляtext post / текстовый постhashtag / хэштегPIN code / PIN-кодsmartphone app / приложение для смартфонаidentity data vault / хранилище данных личностиconfiguration file / файл конфигурацииdirectory / директорияcredentials / учётные данныеencryption / шифрованиеbiometric authentication / биометрическая аутентификацияrate limiting / ограничение частоты попытокcomputer hacking / компьютерный взлом
- @dev_meme / 7932 2026-04-16
- Template
- tweet screenshot
- Type
- image
- Size
- 511×800 · 92.3 KiB
- Mood
- саркастичный, абсурдный
- Language
- en
- Added