Nmap Finds Everything Open
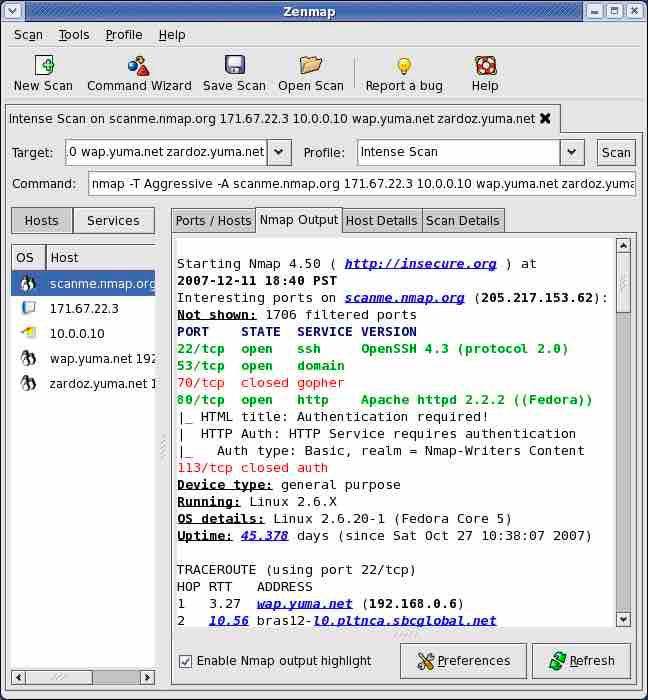
Starting Nmap 4.50 ( http://insecure.org ) at 2007-12-18 18:40 PST Interesting ports on scanme.nmap.org (205.217.153.62): Not shown: 1769 filtered ports PORT STATE SERVICE VERSION 22/tcp open ssh OpenSSH 4.3 (protocol 2.0) 53/tcp open domain 70/tcp closed gopher 80/tcp open http Apache httpd 2.2.2 ((Fedora)) |_ HTML title: Authentication required |_ HTTP Auth: HTTP server requires authentication |_ Auth type: Basic, realm = Nmap-Writers Content 113/tcp closed auth Device type: general purpose Running: Linux 2.6.X OS details: Linux 2.6.20-1 (Fedora Core 5) Uptime: 45.378 days (since Sat Oct 27 10:38:07 2007) TRACEROUTE (using port 22/tcp) HOP RTT ADDRESS 1 3.27 wap.yuma.net (192.168.0.6) 2 10.56 bras12-10.pltnca.sbcglobal.net
A screenshot of the Zenmap network-scanning interface shows an Nmap scan revealing open SSH, DNS, and HTTP ports on a host, along with operating-system and traceroute details. The joke is the exaggeratedly dated software, Fedora system, and surprisingly revealing scan output, making it a nostalgic infosec reaction to an old or poorly secured server. It is used when discussing network reconnaissance, exposed services, legacy infrastructure, or a scan that finds far more information than expected.
network scanner window / окно сетевого сканераdesktop application interface / интерфейс настольного приложенияterminal output / вывод терминалаcomputer monitor / монитор компьютераport scan results / результаты сканирования портовopen padlock icon / значок открытого замкаserver host list / список хостов сервераgreen highlighted text / зелёный выделенный текстscroll bar / полоса прокруткиtraceroute output / вывод трассировки маршрутаSSH service / служба SSHHTTP service / служба HTTPLinux operating system / операционная система LinuxFedora logo / логотип Fedoranetwork addresses / сетевые адреса
- @infosecmemes / 841 2023-07-13
- Type
- image
- Size
- 648×700 · 71.1 KiB
- Mood
- саркастичный, ностальгический
- Language
- en
- Added