SQL Injection Tool Finds Everything
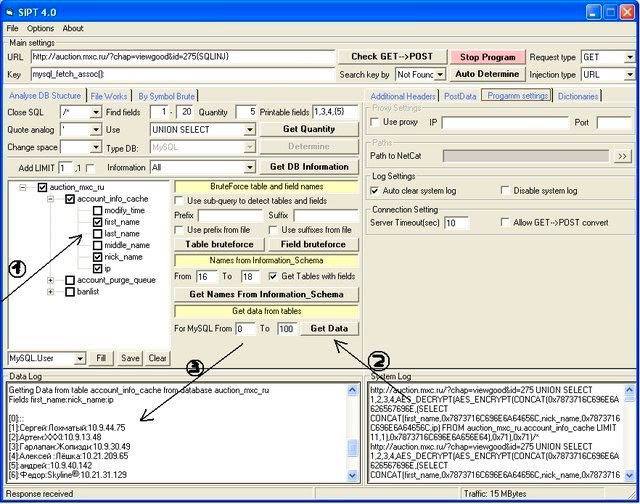
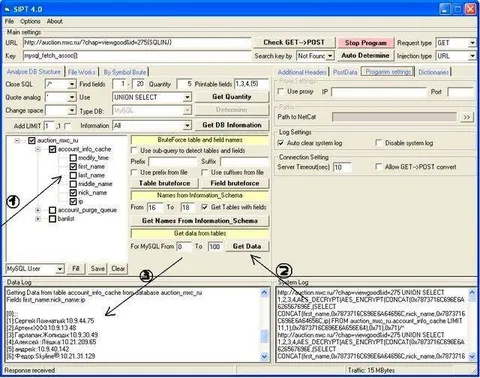
http://auction.mic.ru/?champviewgoodid=275(SQLIN) mysql_fetch_assoc() Search key by Not Found Injection type URL UNION SELECT account_info_cache modify_time first_name last_name middle_name nick_name id account_unique barlist BruteForce table and field names Use sub-query to detect tables and fields Use prefx from file Use suffixes from file Table bruteforce Field bruteforce Names from Information_Schema Get Names From Information_Schema Get data from table For MySQL From 0 To 100 Data Log Getting Data from table account_info_cache from database auction_mic.ru Сергей Похмельный 10.9.44.75 Арсений 10.19.13.9.148 Александр Хохин 10.9.30.9 Алексей Лычко 10.21.209.65 Арсен 10.90.144.21 Федор Скумье 10.21.31.129 System Log http://auction.mic.ru/?champviewgoodid=275 UNION SELECT 26,3,4,5,6,DECAY[,IPT...] Response received
Скриншот старой программы SIFT 4.0 показывает автоматизированный SQL-инъекционный взлом сайта: инструмент перебирает таблицы и поля, а затем выводит содержимое базы данных с именами и IP-адресами. Шутка в том, что атака выглядит чрезмерно простой и почти будничной: достаточно нажать несколько кнопок, чтобы получить чужие данные. Такой мем отправляют как реакцию на небезопасный сайт, плохую защиту базы данных или слишком лёгкий взлом. EN: A screenshot of the old SIFT 4.0 program shows an automated SQL injection attack against a website: the tool brute-forces tables and fields and then displays database contents with names and IP addresses. The joke is that the attack looks absurdly simple and routine: just a few button clicks reveal someone else’s data. People send this meme as a reaction to an insecure website, poor database protection, or an extremely easy hack.
- @infosecmemes / 841 2023-07-13
- Type
- image
- Size
- 640×504 · 71.5 KiB
- Mood
- саркастичный
- Language
- en
- Added