Directory Traversal Vulnerability
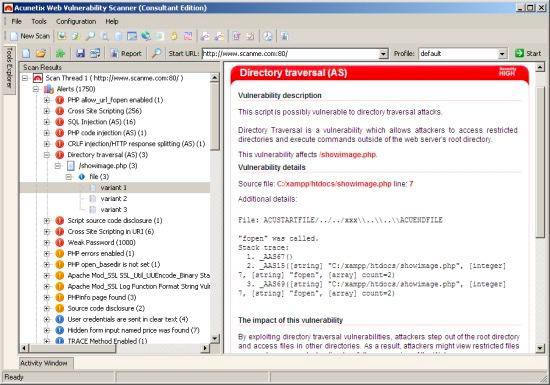
Directory traversal (AS) Vulnerability description This script is possibly vulnerable to directory traversal attacks. Directory Traversal (AS) is a vulnerability which allows attackers to access restricted directories and execute commands outside of the web server's root directory. This vulnerability affects the following page. Vulnerability details Source file: C:\xampp\htdocs\showimage.php line: 7 Additional details: File: ACS.../../../../../../../etc/passwd "open" was called. Stack trace 1. __ASSE... 2. __AS1["option"] <C:\xampp\htdocs\showimage.php", [integer] 3. [string] "open", [array] count=2 The impact of this vulnerability By exploiting directory traversal vulnerabilities, attackers step out of the root directory and access files in other directories.
A screenshot of the Acunetix Web Vulnerability Scanner shows a “Directory traversal (AS)” finding in a PHP image script. The joke is the overly serious security report documenting that a simple image display file can be exploited to access files outside the web server’s root directory. It is used as a reaction to unexpectedly obvious or embarrassing security vulnerabilities. EN: A screenshot of the Acunetix Web Vulnerability Scanner shows a “Directory traversal (AS)” finding in a PHP image script. The joke is the overly serious security report documenting that a simple image display file can be exploited to access files outside the web server’s root directory. It is used as a reaction to unexpectedly obvious or embarrassing security vulnerabilities.
- @infosecmemes / 841 2023-07-13
- Type
- image
- Size
- 550×385 · 42.6 KiB
- Mood
- sarcastic, technical
- Language
- en
- Added