Cisco Security Fix Blocks curl
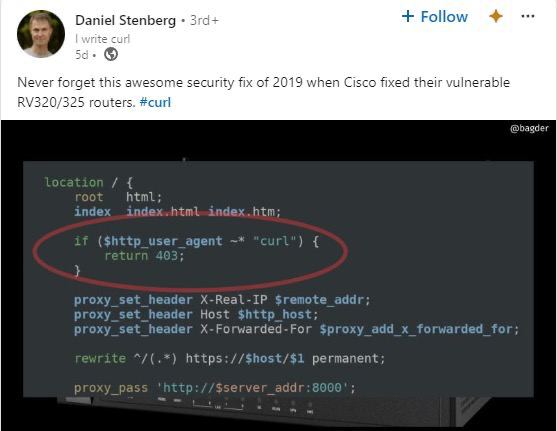
Never forget this awesome security fix of 2019 when Cisco fixed their vulnerable RV320/325 routers. #curl location / { root html; index index.html index.htm; if ($http_user_agent ~* "curl") { return 403; } proxy_set_header X-Real-IP $remote_addr; proxy_set_header Host $host; proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for; rewrite ^/(.*) https://$host/$1 permanent; proxy_pass "http://$server_addr:8000"; }
A screenshot shows a social media post joking about Cisco’s 2019 security fix for vulnerable RV320/325 routers, alongside an Nginx configuration that blocks requests from curl with a 403 response. The punchline is that this absurdly simple user-agent block is presented as an “awesome security fix,” mocking weak or superficial cybersecurity patches. It is used as a reaction to poor security practices, lazy fixes, or incompetent engineering. EN: A screenshot shows a social media post joking about Cisco’s 2019 security fix for vulnerable RV320/325 routers, alongside an Nginx configuration that blocks requests from curl with a 403 response. The punchline is that this absurdly simple user-agent block is presented as an “awesome security fix,” mocking weak or superficial cybersecurity patches. It is used as a reaction to poor security practices, lazy fixes, or incompetent engineering.
- @pokupkabitka / 39225 2024-04-21
- @infosecmemes / 960 2024-04-22
- Type
- image
- Size
- 557×431 · 25.7 KiB
- Mood
- sarcastic
- Language
- en
- Added