Types of Threat-Intel Paper
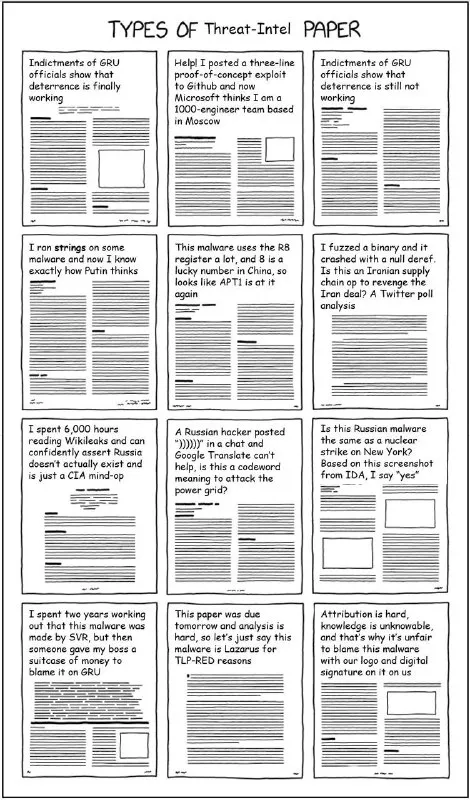
TYPES OF Threat-Intel PAPER Indictments of GRU officials show that deterrence is finally working Help! I posted a three-line proof-of-concept exploit to Github and now Microsoft thinks I am a 1000-engineer team based in Moscow Indictments of GRU officials show that deterrence is still not working I ran strings on some malware and now I know exactly how Putin thinks This malware uses the R8 register a lot, and 8 is a lucky number in China, so it looks like APT 1 again I fuzzed a binary and it crashed with a null deref. Is this an Iranian supply chain or to revenge the Iran deal? A Twitter poll analysis I spent 6,000 hours reading Wikileaks and can confidently assert Russia doesn't actually exist and is just a CIA mind-exop A Russian hacker posted a :)))) in a chat and Google Translate can't help, is this a codeword meaning to attack the power grid? Is this Russian malware the same as a nuclear strike on New York? Based on this screenshot from IDA, I say 'yes' I spent two years working out that this malware was made by SVR, but then someone gave my boss a suitcase of money to blame it on GRU This paper was due tomorrow and analysis found so let's just say this malware is Lazarus for TLP-RED reasons Attribution is hard, knowledge is unknowable, and that's why it's unfair to blame this malware with our logo and digital signature on it on us
A twelve-panel comic presents absurd examples of threat-intelligence papers, including overconfident attribution based on tiny clues, geopolitical speculation, and blatant excuses. The joke mocks cybersecurity analysts who turn weak technical evidence into dramatic claims about Russia, Iran, China, or North Korea, while also showing how deadlines, politics, and uncertainty distort malware attribution.
threat-intelligence papers / документы по анализу угрозcomic panels / панели комиксаprinted reports / распечатанные отчётыtext paragraphs / абзацы текстаmalware analysis / анализ вредоносного ПОcomputer code / компьютерный кодbinary file / двоичный файлnull dereference / разыменование nullTwitter poll / опрос в Twitterpower grid / электросетьnuclear explosion diagram / схема ядерного взрываMoscow reference / упоминание МосквыRussian flag reference / упоминание российского флагаdigital signature / цифровая подписьlogo / логотипsuitcase of money / чемодан денегhandwritten annotations / рукописные пометки
- @infosecmemes / 600 2021-05-04
- Type
- image
- Size
- 470×800 · 117.4 KiB
- Mood
- sarcastic, absurd
- Language
- en
- Added