Known-Invalid Kernel Patches
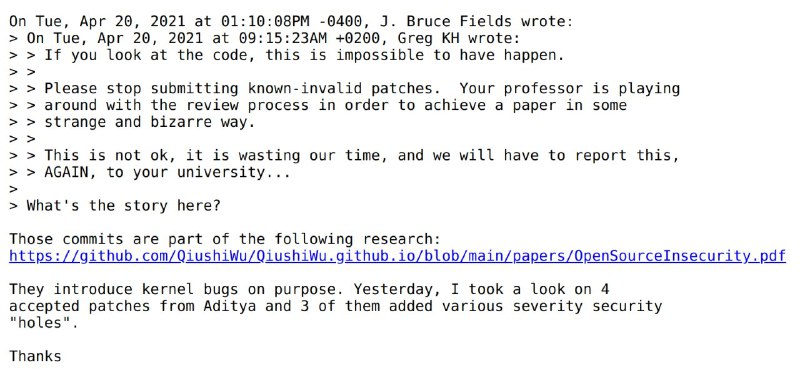
On Tue, Apr 20, 2021 at 01:10:08PM -0400, J. Bruce Fields wrote: > On Tue, Apr 20, 2021 at 09:15:23AM +0200, Greg KH wrote: > > If you look at the code, this is impossible to have happen. > > > > Please stop submitting known-invalid patches. Your professor is playing > > > around with the review process in order to achieve a paper in some > > > strange and bizarre way. > > > > > > This is not ok, it is wasting our time, and we will have to report this, > > > AGAIN, to your university... > > > > > What's the story here? Those commits are part of the following research: https://github.com/QiushiWu/QiushiWu.github.io/blob/main/papers/OpenSourceInsecurity.pdf They introduce kernel bugs on purpose. Yesterday, I took a look on 4 accepted patches from Aditya and 3 of them added various severity security "holes". Thanks
A screenshot of an email thread shows Linux kernel maintainers discussing intentionally submitting invalid patches and questioning a university research project. The punchline is that the suspicious commits were allegedly part of research that deliberately introduced security holes, making the earlier accusation unexpectedly accurate. It is shared as a reaction to bizarre technical explanations, malicious testing, or academic projects that create the problem they claim to study. EN: A screenshot of an email thread shows Linux kernel maintainers discussing intentionally submitting invalid patches and questioning a university research project. The punchline is that the suspicious commits were allegedly part of research that deliberately introduced security holes, making the earlier accusation unexpectedly accurate. It is shared as a reaction to bizarre technical explanations, malicious testing, or academic projects that create the problem they claim to study.
- @infosecmemes / 595 2021-04-21
- Type
- image
- Size
- 800×376 · 69.3 KiB
- Mood
- sarcastic, absurd
- Language
- en
- Added