AES-GCM Two Plaintexts Attack
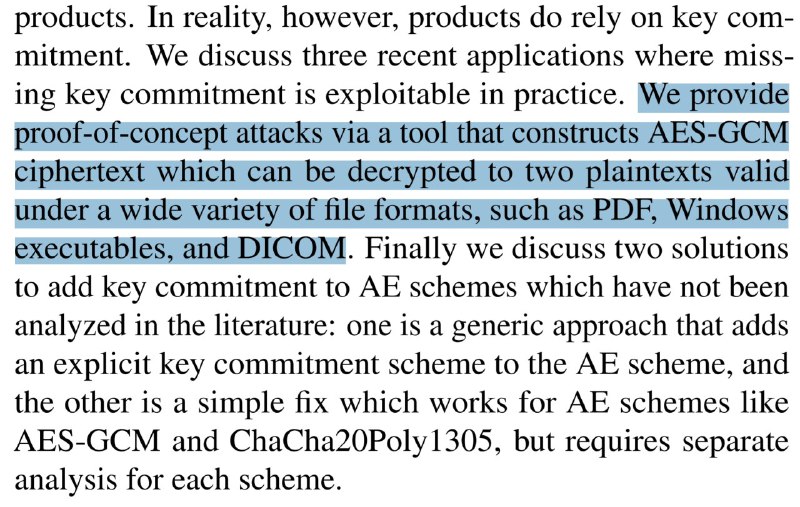
products. In reality, however, products do rely on key com- mitment. We discuss three recent applications where miss- ing key commitment is exploitable in practice. We provide proof-of-concept attacks via a tool that constructs AES-GCM ciphertext which can be decrypted to two plaintexts valid under a wide variety of file formats, such as PDF, Windows executables, and DICOM. Finally we discuss two solutions to add key commitment to AE schemes which have not been analyzed in the literature: one is a generic approach that adds an explicit key commitment scheme to the AE scheme, and the other is a simple fix which works for AE schemes like AES-GCM and ChaCha20Poly1305, but requires separate analysis for each scheme.
A cropped academic paper page highlights a passage about proof-of-concept attacks that create AES-GCM ciphertext decryptable into two valid plaintexts, including PDFs, Windows executables, and DICOM files. The joke is the absurdly alarming security finding presented in dry research-paper language, making it a fitting reaction for cryptography and infosecurity discussions. EN: A cropped academic paper page highlights a passage about proof-of-concept attacks that create AES-GCM ciphertext decryptable into two valid plaintexts, including PDFs, Windows executables, and DICOM files. The joke is the absurdly alarming security finding presented in dry research-paper language, making it a fitting reaction for cryptography and infosecurity discussions.
- @infosecmemes / 503 2020-12-16
- Type
- image
- Size
- 800×507 · 131.7 KiB
- Mood
- dryly alarming
- Language
- en
- Added