Exploitation Trends in Security
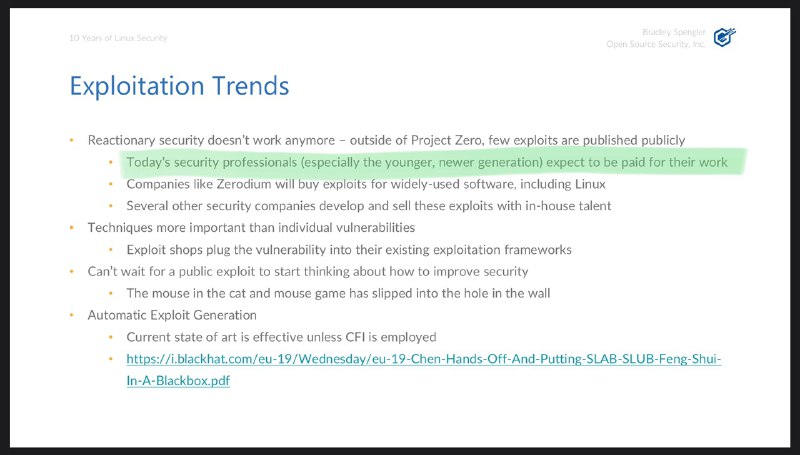
10 Years of Linux Security Exploitation Trends Reactionary security doesn’t work anymore – outside of Project Zero, few exploits are published publicly Today’s security professionals (especially the younger, newer generation) expect to be paid for their work Companies like Zerodium will buy exploits for widely-used software, including Linux Several other security companies develop and sell these exploits with in-house talent Techniques more important than individual vulnerabilities Exploit shops plug the vulnerability into their existing exploitation frameworks Can’t wait for a public exploit to start thinking about how to improve security The mouse in the cat and mouse game has slipped into the hole in the wall Automatic Exploit Generation Current state of art is effective unless CFI is employed https://i.blackhat.com/eu-19/Wednesday/eu-19-Chen-Hands-Off-And-Putting-SLAB-SLUB-Feng-Shui-In-A-Blackbox.pdf
A screenshot of a presentation slide titled “Exploitation Trends” discusses how exploit development has shifted toward paid security professionals, exploit shops, reusable frameworks, and automatic exploit generation. The joke is the line about the mouse slipping into the hole: attackers and defenders are playing cat and mouse, but the attacker has escaped into a place where traditional defensive reactions no longer work. It is used as a reaction to changing cybersecurity economics and increasingly sophisticated exploitation techniques.
presentation slide / слайд презентацииprojector screen / экран проектораbullet points / пункты спискаgreen highlight / зелёная подсветкаblue heading / синий заголовокcomputer security text / текст о компьютерной безопасностиhyperlink / гиперссылкаmouse / мышьcat / кошкаhole in a wall / дыра в стенеLinux logo / логотип Linuxblack background / чёрный фон
- @infosecmemes / 294 2020-07-03
- Type
- image
- Size
- 800×455 · 52.4 KiB
- Mood
- sarcastic, technical
- Language
- en
- Added