Bug Bounty Rejected by Design
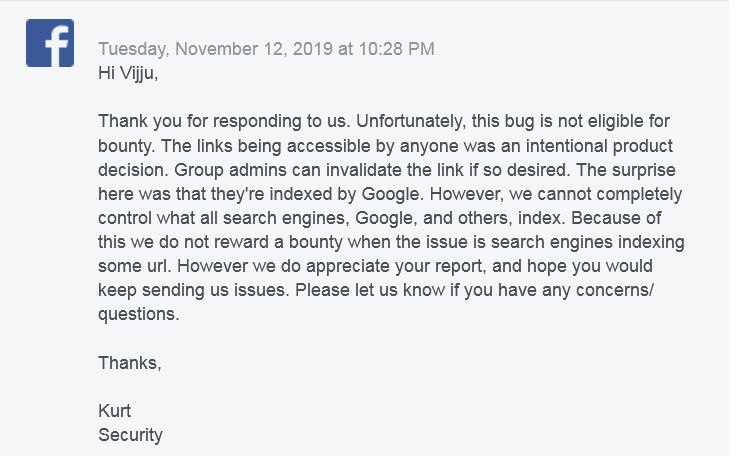
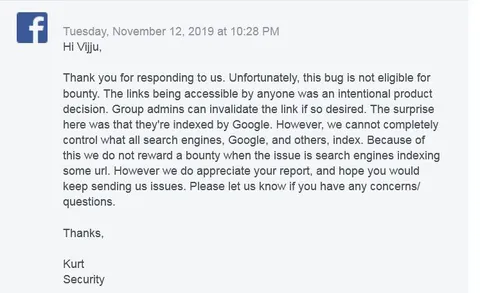
Tuesday, November 12, 2019 at 10:28 PM Hi Vijju, Thank you for responding to us. Unfortunately, this bug is not eligible for bounty. The links being accessible by anyone was an intentional product decision. Group admins can invalidate the link if so desired. The surprise here was that they're indexed by Google. However, we cannot completely control what all search engines. Google, and others, index. Because of this we do not reward a bounty when the issue is search engines indexing some url. However we do appreciate your report, and hope you would keep sending us issues. Please let us know if you have any concerns/questions. Thanks, Kurt Security
A Facebook-style screenshot shows a security team replying to a bug report about publicly accessible links. They explain that the access was intentional and refuse a bounty, while acknowledging that Google indexing the links was unexpected. The joke is the absurdly dismissive bug-bounty response to a seemingly serious security issue. EN: A Facebook-style screenshot shows a security team replying to a bug report about publicly accessible links. They explain that the access was intentional and refuse a bounty, while acknowledging that Google indexing the links was unexpected. The joke is the absurdly dismissive bug-bounty response to a seemingly serious security issue.
social media post / публикация в соцсетиFacebook logo / логотип Facebooksecurity report / отчёт о безопасностиcomputer screen / экран компьютераtext message / текстовое сообщениеbug bounty / вознаграждение за багhyperlink / гиперссылкаGoogle search engine / поисковая система Googlegroup admin / администратор группыemail-style reply / ответ в стиле электронного письма
- @infosecmemes / 194 2020-02-21
- Type
- image
- Size
- 747×456 · 52.0 KiB
- Mood
- sarcastic, absurd
- Language
- en
- Added