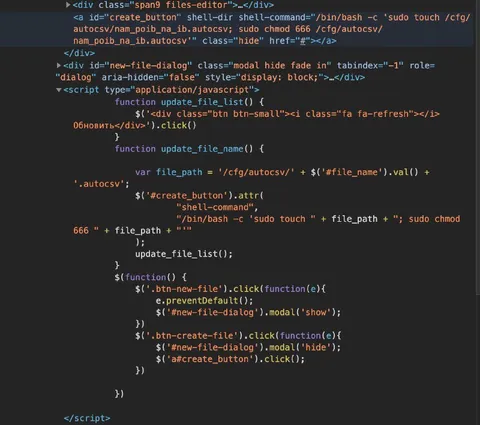
sudo touch и chmod 666
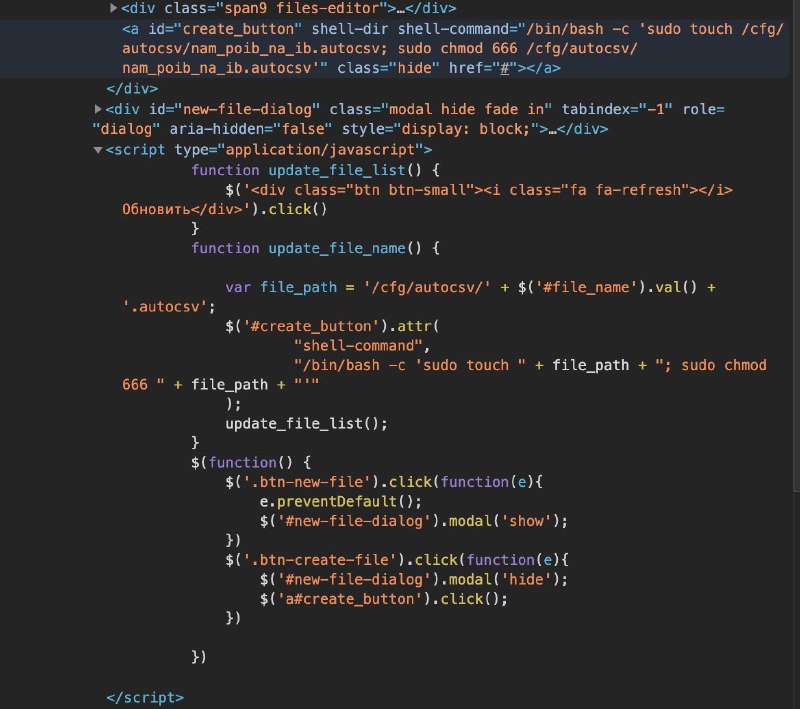
<div class="span9 files-editor">...</div> <a id="create_button" shell-command="/bin/bash -c 'sudo touch /cfg/autocsv/nam_poib_na_ib.autocsv; sudo chmod 666 /cfg/autocsv/nam_poib_na_ib.autocsv'" class="hide" href="#"></a> </div> <div id="new-file-dialog" class="modal hide fade in" tabindex="-1" role="dialog" aria-hidden="false" style="display: block;">...</div> <script type="application/javascript"> function update_file_list() { $('#file-list').html('<i class="fa fa-refresh"></i> Обновить</div>').click(function(){ } function update_file_name() { var file_path = '/cfg/autocsv/' + $('#file_name').val() + '.autocsv'; $('#create_button').attr( "shell-command", "/bin/bash -c 'sudo touch " + file_path + "; sudo chmod 666 " + file_path + "'" ); update_file_list(); } $(function() { $('.btn-new-file').click(function(e){ e.preventDefault(); $('#new-file-dialog').modal('show'); }); $('.btn-create-file').click(function(e){ $('#new-file-dialog').modal('hide'); $('#create_button').click(); }); }); </script>
На скриншоте показан фрагмент веб-интерфейса и JavaScript-кода для создания файла, где используется команда sudo touch и выдаются права chmod 666. Шутка основана на небезопасной настройке прав доступа: разработчик буквально создаёт файл, доступный для чтения и записи всем пользователям. Такой мем отправляют как реакцию на плохую практику информационной безопасности или уязвимый код. EN: The screenshot shows part of a web interface and JavaScript code for creating a file, using sudo touch and assigning chmod 666 permissions. The joke is based on an insecure permission setting: the developer literally creates a file that is readable and writable by everyone. This meme is shared as a reaction to poor information-security practices or vulnerable code.
- @infosecmemes / 113 2019-11-20
- Type
- image
- Size
- 800×709 · 90.2 KiB
- Mood
- саркастичный, абсурдный
- Language
- ru
- Added