SQL Injection Six-Year Bounty
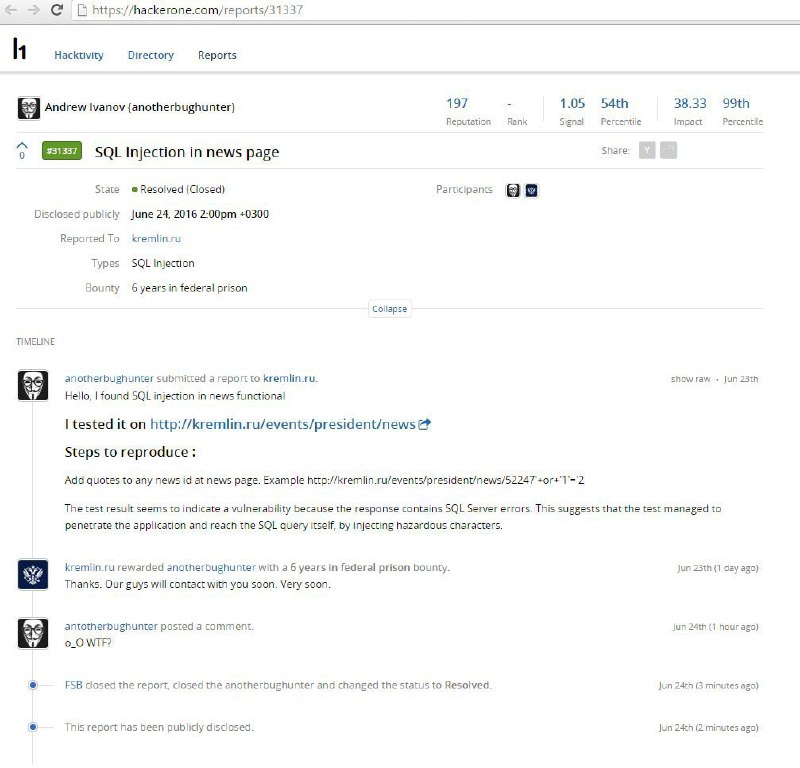
SQL Injection in news page Resolved (Closed) Disclosed publicly June 24, 2016 2:00pm +0300 Reported To kremlin.ru Types SQL Injection Bounty 6 years in federal prison anotherbughunter submitted a report to kremlin.ru. Hello, I found SQL injection in news functional I tested it on http://kremlin.ru/events/president/news Steps to reproduce: Add quotes to any news id at news page. Example http://kremlin.ru/events/president/news/52247: 'or 1=2 The test result seems to indicate a vulnerability because the response contains SQL Server errors. This suggests that the test managed to penetrate the application and reach the SQL query itself, by injecting hazardous characters. kremlin.ru rewarded anotherbughunter with a 6 years in federal prison bounty. Thanks. Our guys will contact you soon. Very soon. o_O WTF? FSB closed the report, closed the anotherbughunter and changed the status to Resolved. This report has been publicly disclosed.
A screenshot of a HackerOne-style bug bounty report shows a hacker reporting SQL injection on the Kremlin website. Instead of receiving money, the hacker is supposedly rewarded with six years in a federal prison, and the FSB closes both the report and the hacker. The joke relies on the contrast between legitimate bug bounty procedures and the danger of exposing a vulnerability in a government website. EN: A screenshot of a HackerOne-style bug bounty report shows a hacker reporting SQL injection on the Kremlin website. Instead of receiving money, the hacker is supposedly rewarded with six years in a federal prison, and the FSB closes both the report and the hacker. The joke relies on the contrast between legitimate bug bounty procedures and the danger of exposing a vulnerability in a government website.
- Template
- HackerOne bug bounty report screenshot
- Type
- image
- Size
- 800×768 · 75.3 KiB
- Mood
- darkly humorous
- Language
- en
- Added