Two Libraries One CUPS
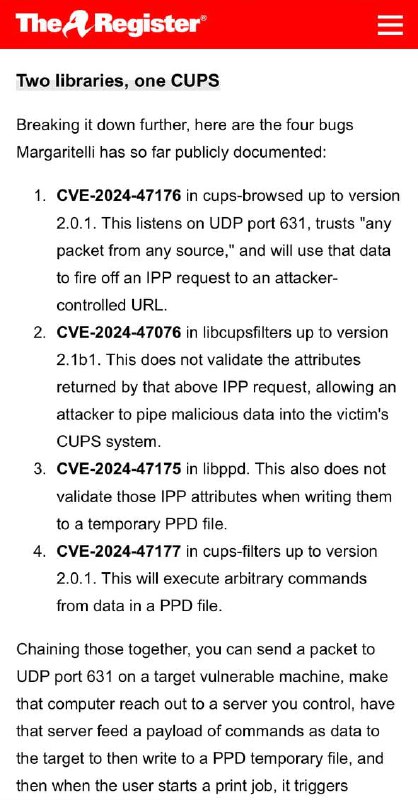
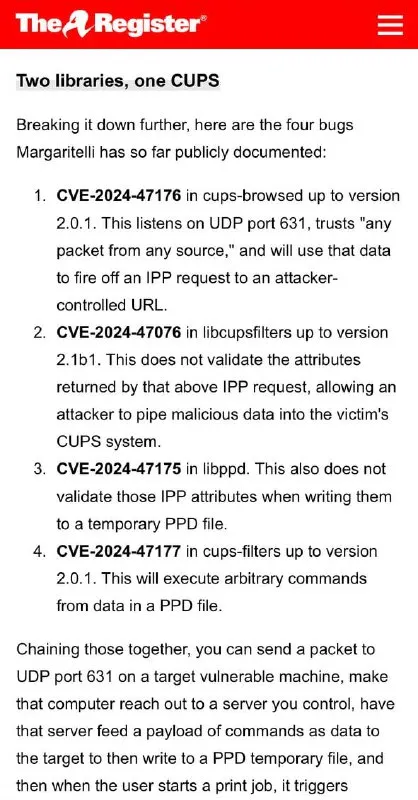
The A Register® Two libraries, one CUPS Breaking it down further, here are the four bugs Margarettelli has so far publicly documented: 1. CVE-2024-47176 in cups-browsed up to version 2.0.1. This listens on UDP port 631, trusts "any packet from any source," and will use that data to fire off an IPP request to an attacker-controlled URL. 2. CVE-2024-47076 in libcup sfilters up to version 2.1b1. This does not validate the attributes returned by that above IPP request, allowing an attacker to pipe malicious data into the victim's CUPS system. 3. CVE-2024-47175 in libppd. This also does not validate those IPP attributes when writing them to a temporary PPD file. 4. CVE-2024-47177 in cups-filters up to version 2.0.1. This will execute arbitrary commands from data in a PPD file. Chaining those together, you can send a packet to UDP port 631 on a target vulnerable machine, make that computer reach out to a server you control, have that server feed a payload of commands as data to the target to then write to a PPD temporary file, and then when the user starts a print job, it triggers
The image is a screenshot of a technology article from The A Register titled “Two libraries, one CUPS.” It lists four vulnerabilities in the Linux printing system and explains how they can be chained into remote command execution when a user starts a print job. The joke is the pun on “CUPS” and “cups,” presenting a serious security exploit as “two libraries, one CUPS.”
article screenshot / скриншот статьиred website header / красная шапка сайтаThe A Register logo / логотип The A Registerhamburger menu icon / значок меню-гамбургераblack headline text / чёрный текст заголовкаnumbered list / нумерованный списокparagraph text / текст абзацаCVE vulnerability identifiers / идентификаторы уязвимостей CVEcomputer security article / статья о компьютерной безопасностиprinting system / система печатиprinter software / программное обеспечение принтераnetwork packet / сетевой пакетserver / серверcommand payload / полезная нагрузка командPPD file / PPD-файл
#cybersecurity#кибербезопасность#computer security#компьютерная безопасность#vulnerability#уязвимость#cups#linux#линукс#printing#печать#hacking#хакерство#remote code execution#удалённое выполнение кода#exploit#эксплойт#article#статья#screenshot#скриншот#tech humor#технический юмор#security news#новости безопасности
- @ithueti / 14110 2024-09-27
- Type
- image
- Size
- 418×800 · 88.1 KiB
- Mood
- technical, ironic
- Language
- en
- Added