Critical curl vulnerability announcement
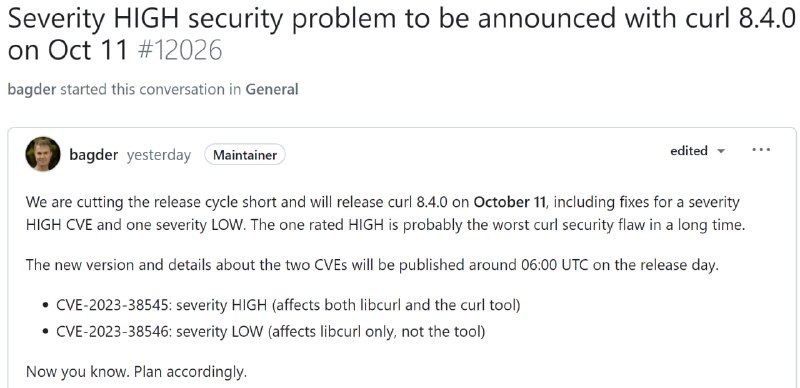
Severity HIGH security problem to be announced with curl 8.4.0 on Oct 11 #12026 badger started this conversation in General badger yesterday Maintainer We are cutting the release cycle short and will release curl 8.4.0 on October 11, including fixes for a severity HIGH CVE and one severity LOW. The one rated HIGH is probably the worst curl security flaw in a long time. The new version and details about the two CVEs will be published around 06:00 UTC on the release day. • CVE-2023-38545: severity HIGH (affects both libcurl and the curl tool) • CVE-2023-38546: severity LOW (affects libcurl only, not the tool) Now you know. Plan accordingly.
A screenshot of a software development discussion announces that curl 8.4.0 will contain fixes for one critical and one low-severity CVE, with the details deliberately scheduled for release day. The joke is that users are told about a potentially serious security flaw only shortly before the announcement, leaving little time to prepare; it is used as a reaction to delayed vulnerability disclosure and poor advance warning. EN: A screenshot of a software development discussion announces that curl 8.4.0 will contain fixes for one critical and one low-severity CVE, with the details deliberately scheduled for release day. The joke is that users are told about a potentially serious security flaw only shortly before the announcement, leaving little time to prepare; it is used as a reaction to delayed vulnerability disclosure and poor advance warning.
- @ithueti / 10513 2023-10-05
- Type
- image
- Size
- 800×388 · 54.5 KiB
- Mood
- sarcastic
- Language
- en
- Added