Attackers Found a Large Uptime Window
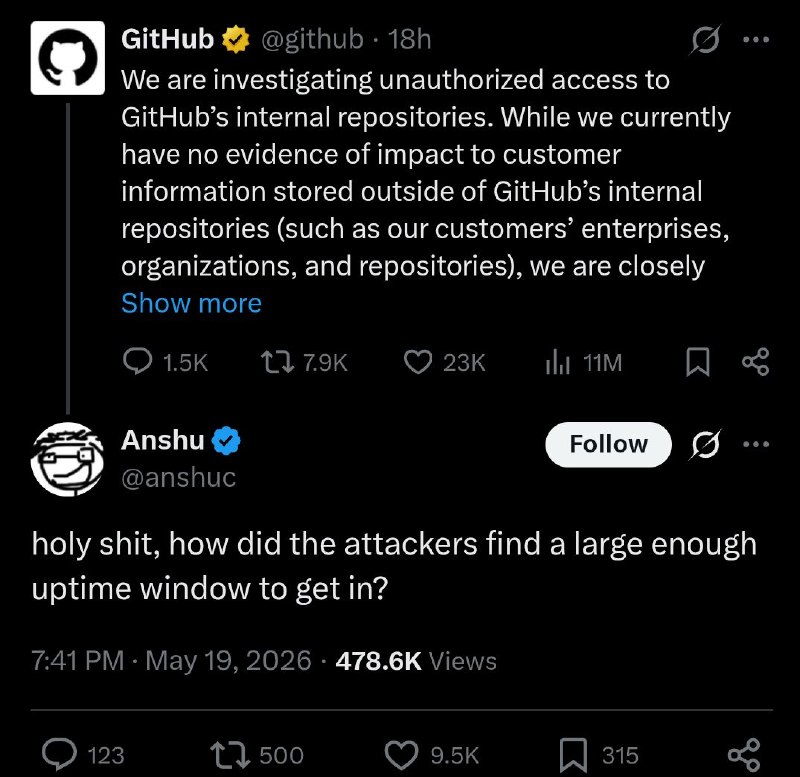
We are investigating unauthorized access to GitHub’s internal repositories. While we currently have no evidence of impact to customer information stored outside of GitHub’s internal repositories (such as our customers’ enterprises, organizations, and repositories), we are closely holy shit, how did the attackers find a large enough uptime window to get in?
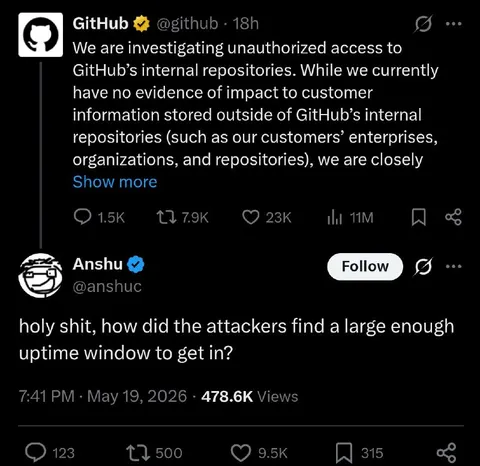
A screenshot shows GitHub announcing an investigation into unauthorized access, followed by a sarcastic reply asking how attackers found a sufficiently large “uptime window” to break in. The joke treats uptime as if it were a security vulnerability or an open time window, poking fun at the absurdity of the breach announcement. EN: A screenshot shows GitHub announcing an investigation into unauthorized access, followed by a sarcastic reply asking how attackers found a sufficiently large “uptime window” to break in. The joke treats uptime as if it were a security vulnerability or an open time window, poking fun at the absurdity of the breach announcement.
social media post / пост в соцсетиGitHub logo / логотип GitHubblack interface / чёрный интерфейсprofile avatar / аватар профиляverified badge / значок верификацииreply tweet / ответный твитsecurity announcement / объявление о безопасностиtext block / текстовый блокengagement icons / иконки реакцийview count / счётчик просмотров
- Type
- image
- Size
- 800×777 · 98.3 KiB
- Mood
- sarcastic, absurd
- Language
- en
- Added