How the Attack Worked
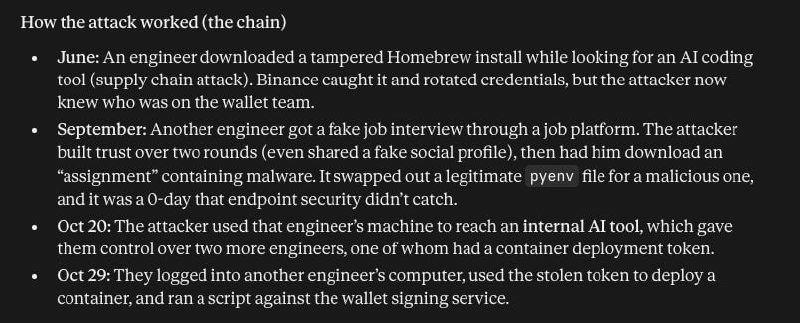
How the attack worked (the chain) • June: An engineer downloaded a tampered Homebrew install while looking for an AI coding tool (supply chain attack). Binance caught it and rotated credentials, but the attacker now knew who was on the wallet team. • September: Another engineer got a fake job interview through a job platform. The attacker built trust over two rounds (even shared a fake social profile), then had him download an “assignment” containing malware. It swapped out a legitimate pyenv file for a malicious one, and it was a 0-day that endpoint security didn’t catch. • Oct 20: The attacker used that engineer’s machine to reach an internal AI tool, which gave them control over two more engineers, one of whom had a container deployment token. • Oct 29: They logged into another engineer’s computer, used the stolen token to deploy a container, and ran a script against the wallet signing service.
The image is a dark text panel titled “How the attack worked (the chain)” and lays out a multi-stage cyberattack: a tampered Homebrew install, a fake job interview, malware hidden in a pyenv file, and stolen credentials and tokens used to reach wallet infrastructure. The joke is the grimly methodical escalation, showing how one compromised engineer led to access to more engineers and eventually the wallet signing service. It is shared as a reaction to supply-chain attacks, social engineering, and security failures that unfold step by step.
dark text panel / тёмная текстовая панельwhite text / белый текстbullet-point list / маркированный списокcomputer / компьютерengineer / инженерAI coding tool / ИИ-инструмент для программированияHomebrew installation / установка Homebrewjob interview / собеседованиеjob platform / платформа поиска работыsocial media profile / профиль в социальной сетиmalware / вредоносная программаsoftware file / файл программного обеспеченияsecurity system / система безопасностиcontainer / контейнерaccess token / токен доступаwallet / кошелёкwallet signing service / сервис подписи кошелька
#кибербезопасность#cybersecurity#атака на цепочку поставок#supply chain attack#социальная инженерия#social engineering#вредоносное по#malware#взлом#hacking#хакеры#hackers#инженеры#engineers#уязвимость#vulnerability#токен доступа#access token#криптокошелёк#crypto wallet#инцидент безопасности#security incident#технологии#technology#реакция#reaction#текстовый мем#text meme#скриншот#screenshot#сарказм#sarcasm
- @ithueti / 19089 2026-11-04
- Type
- image
- Size
- 800×323 · 75.6 KiB
- Mood
- тревожный, саркастичный
- Language
- en
- Added