Ridiculous Open Redirect Bug Report
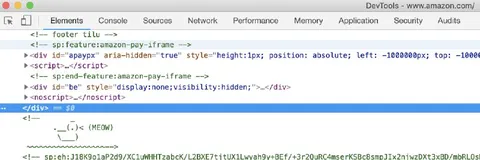
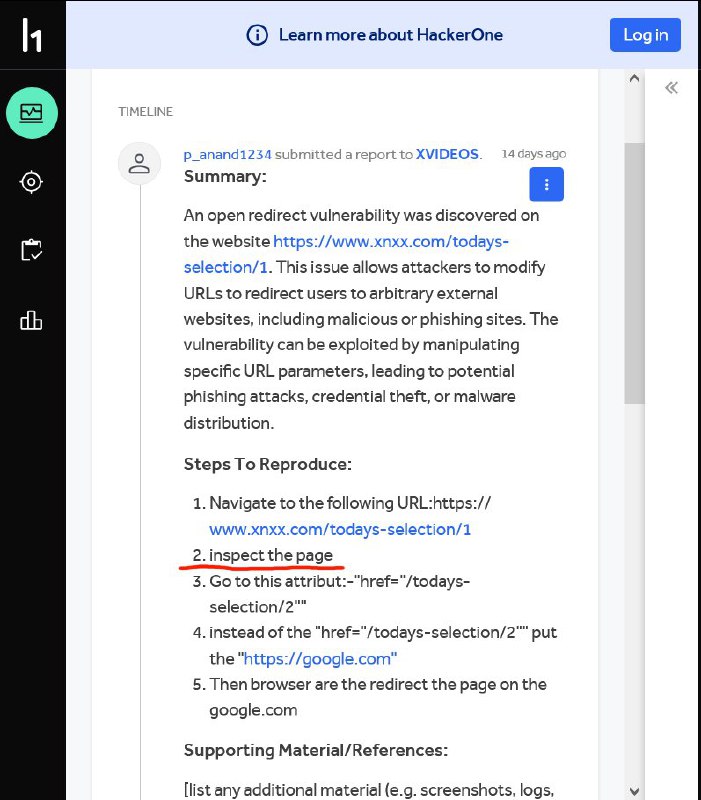
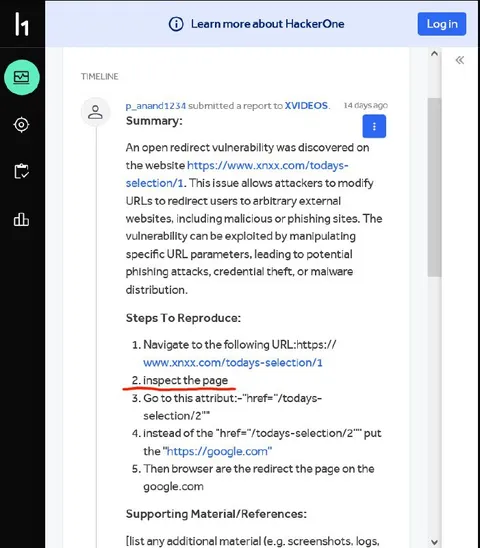
p_anand1234 submitted a report to XVIDEOS. Summary: An open redirect vulnerability was discovered on the website https://www.xnxx.com/todays-selection/1. This issue allows attackers to modify URLs to redirect users to arbitrary external websites, including malicious or phishing sites. The vulnerability can be exploited by manipulating specific URL parameters, leading to potential phishing attacks, credential theft, or malware distribution. Steps To Reproduce: 1. Navigate to the following URL:https://www.xnxx.com/todays-selection/1 2. inspect the page 3. Go to this "attrib:="href="/todays-selection/2"" 4. instead of the "href="/todays-selection/2"" put the "https://google.com" 5. Then browser are the redirect the page on the google.com Supporting Material/References: [list any additional material (e.g. screenshots, logs,
A screenshot of a HackerOne-style vulnerability report claiming that a page can be redirected by changing a URL attribute. The joke is that the report uses an adult-site domain and describes an extremely obvious, trivial redirect to Google with awkward wording, parodying low-quality bug bounty submissions.
- @gentoomemes / 15925 2025-02-10
- @memstash32 / 484 2025-02-10
- Type
- image
- Size
- 701×800 · 90.3 KiB
- Mood
- sarcastic, absurd
- Language
- en
- Added