Quantum-Vulnerable Signature Algorithms
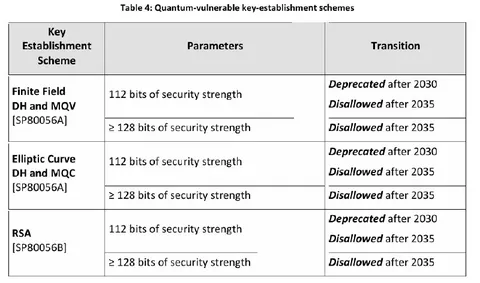
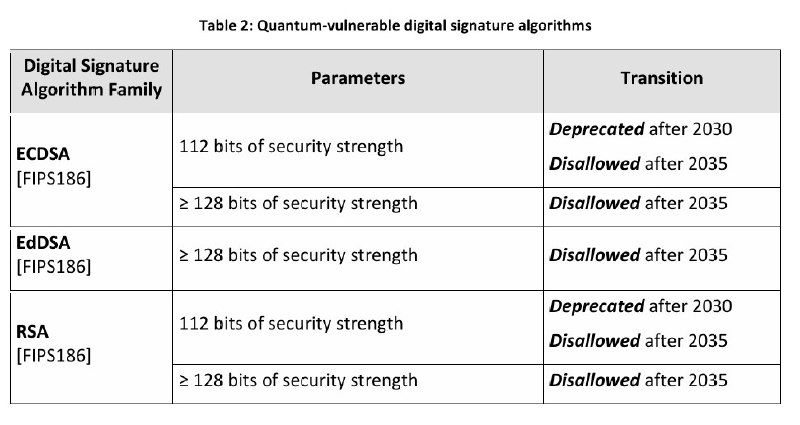
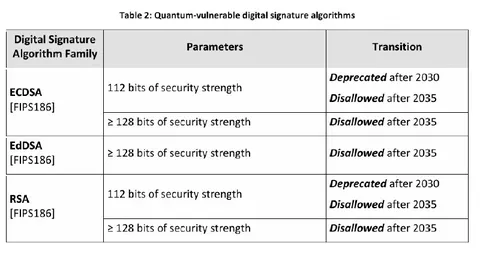
Table 2: Quantum-vulnerable digital signature algorithms Digital Signature Algorithm Family Parameters Transition ECDSA [FIPS186] 112 bits of security strength Deprecated after 2030 Disallowed after 2035 ≥ 128 bits of security strength Disallowed after 2035 EdDSA [FIPS186] ≥ 128 bits of security strength Disallowed after 2035 RSA [FIPS186] 112 bits of security strength Deprecated after 2030 Disallowed after 2035 ≥ 128 bits of security strength Disallowed after 2035
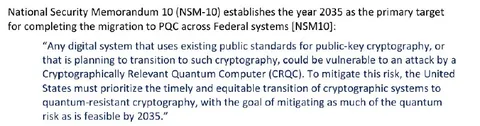
A screenshot of a technical NIST table listing ECDSA, EdDSA, and RSA digital signature algorithms and their post-quantum transition deadlines. The joke is the alarmed reaction to familiar cryptographic standards being deprecated after 2030 and disallowed after 2035, matching the uploader’s “WTF” response.
technical table / техническая таблицаdigital signature algorithms / алгоритмы цифровой подписиECDSA label / обозначение ECDSAEdDSA label / обозначение EdDSARSA label / обозначение RSAsecurity strength parameters / параметры криптографической стойкостиtransition deadlines / сроки переходаgray table header / серый заголовок таблицыgrid lines / линии сеткиbold italic text / полужирный курсивный текст
- @dev_meme / 6392 2024-11-20
- Type
- image
- Size
- 800×425 · 56.2 KiB
- Mood
- alarmed, absurd
- Language
- en
- Added