AWS Authorization Nightmare
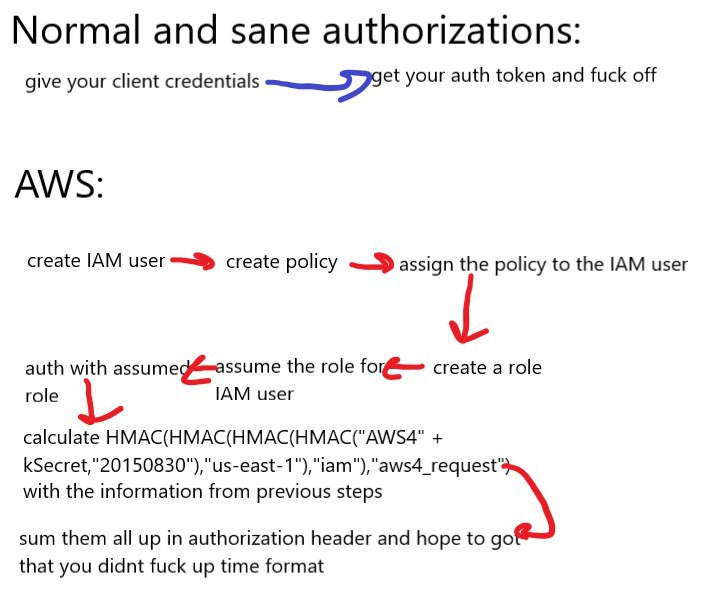
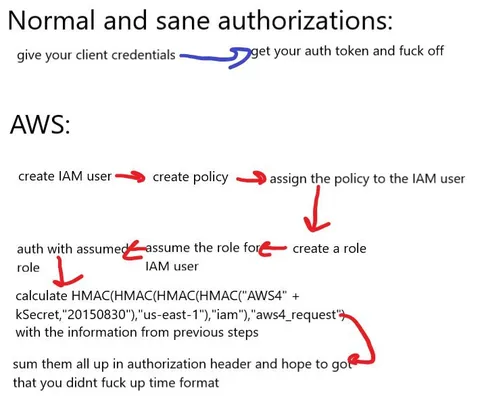
Normal and sane authorizations: give your client credentials get your auth token and fuck off AWS: create IAM user create policy assign the policy to the IAM user create a role assume the role for IAM user auth with assumed role calculate HMAC(HMAC(HMAC(HMAC("AWS4" + kSecret,"20150830"),"us-east-1"),"iam"),"aws4_request") with the information from previous steps sum them all up in authorization header and hope to get that you didnt fuck up time format
The meme contrasts a simple, sensible authorization flow with AWS authentication. Instead of receiving a token and moving on, AWS requires creating users, policies, and roles, then calculating a deeply nested HMAC signature and assembling an authorization header. The punchline is that the process is absurdly complicated and easy to get wrong, especially the time format.
text captions / текстовые подписиblue arrows / синие стрелкиred arrows / красные стрелкиIAM user / пользователь IAMauthorization token / токен авторизацииpolicy / политикаrole / рольauthentication flow / процесс аутентификацииHMAC formula / формула HMACauthorization header / заголовок авторизацииAWS request / запрос AWSwhite background / белый фон
- @dev_meme / 5032 2022-11-24
- @right_wing_dev_squads / 11105 2024-12-14
- Type
- image
- Size
- 710×599 · 55.1 KiB
- Mood
- sarcastic, frustrated
- Language
- en
- Added