AI-Generated Security Reports Banned
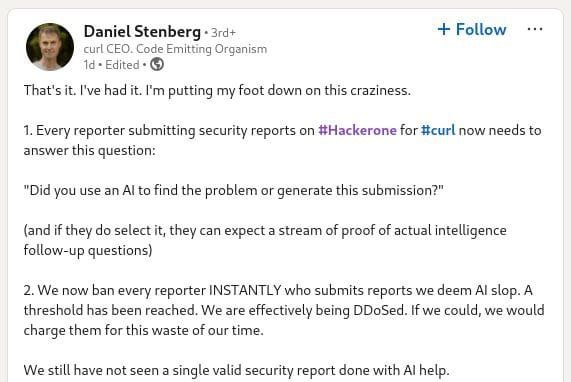
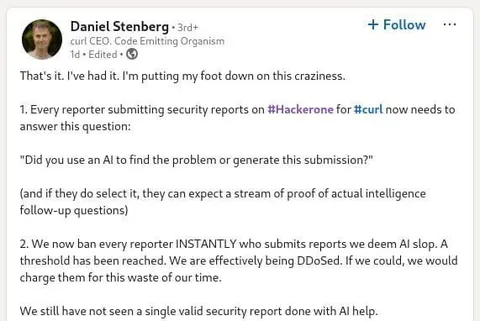
That's it. I've had it. I'm putting my foot down on this craziness. 1. Every reporter submitting security reports on #Hackerone for #curl now needs to answer this question: "Did you use an AI to find the problem or generate this submission?" (and if they do select it, they can expect a stream of proof of actual intelligence follow-up questions) 2. We now ban every reporter INSTANTLY who submits reports we deem AI slop. A threshold has been reached. We are effectively being DDoSed. If we could, we would charge them for this waste of our time. We still have not seen a single valid security report done with AI help.
A screenshot of a LinkedIn post by Daniel Stenberg, the curl maintainer, declaring that security researchers submitting reports to HackerOne for curl must disclose whether they used AI. He jokes that AI-generated “slop” reports are flooding the project like a DDoS and threatens instant bans, while the punchline is the sarcastic demand for proof of “actual intelligence.” This is used as a reaction to frustration with low-quality AI-generated work and spam. EN: A screenshot of a LinkedIn post by Daniel Stenberg, the curl maintainer, declaring that security researchers submitting reports to HackerOne for curl must disclose whether they used AI. He jokes that AI-generated “slop” reports are flooding the project like a DDoS and threatens instant bans, while the punchline is the sarcastic demand for proof of “actual intelligence.” This is used as a reaction to frustration with low-quality AI-generated work and spam.
- @gentoomemes / 17162 2025-05-06
- Type
- image
- Size
- 571×382 · 34.7 KiB
- Mood
- sarcastic, frustrated
- Language
- en
- Added