Cisco’s Curl Security Fix
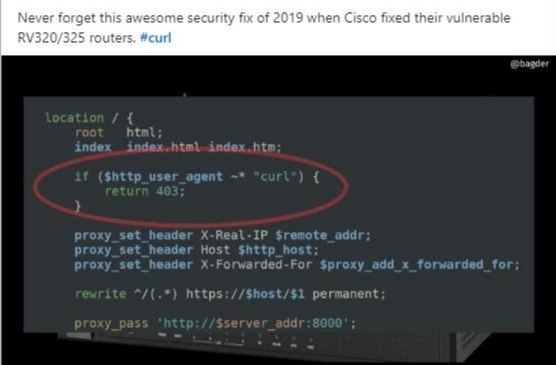
Never forget this awesome security fix of 2019 when Cisco fixed their vulnerable RV320/325 routers. #curl location / { root html; index index.html index.htm; if ($http_user_agent ~* "curl") { return 403; } proxy_set_header X-Real-IP $remote_addr; proxy_set_header Host $http_host; proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for; rewrite ^/(.*) https://$host/$1 permanent; proxy_pass "http://$server_addr:8000";
A screenshot shows an Nginx-style configuration allegedly presented as Cisco’s 2019 security fix for vulnerable RV320/325 routers. The joke is that the “fix” simply blocks requests whose user agent is curl, making the security measure absurdly superficial and easy to bypass.
code screenshot / скриншот кодаrouter configuration / конфигурация маршрутизатораCisco router / маршрутизатор Ciscoserver code / серверный кодterminal-style interface / интерфейс в стиле терминалаdark code editor / тёмный редактор кодаred oval annotation / красная овальная пометкаHTTP request / HTTP-запросweb server / веб-серверsecurity fix / исправление безопасности
- @right_wing_dev_squads / 12806 2025-08-30
- Type
- image
- Size
- 556×365 · 24.4 KiB
- Mood
- sarcastic, absurd
- Language
- en
- Added