Malicious LLM Router Attack
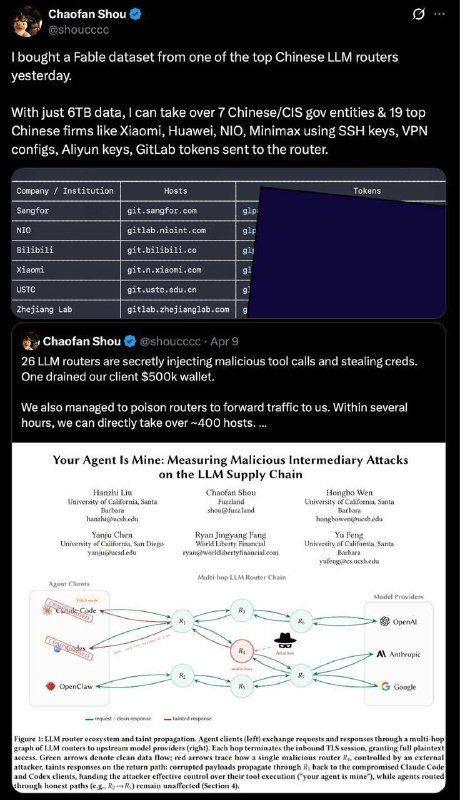
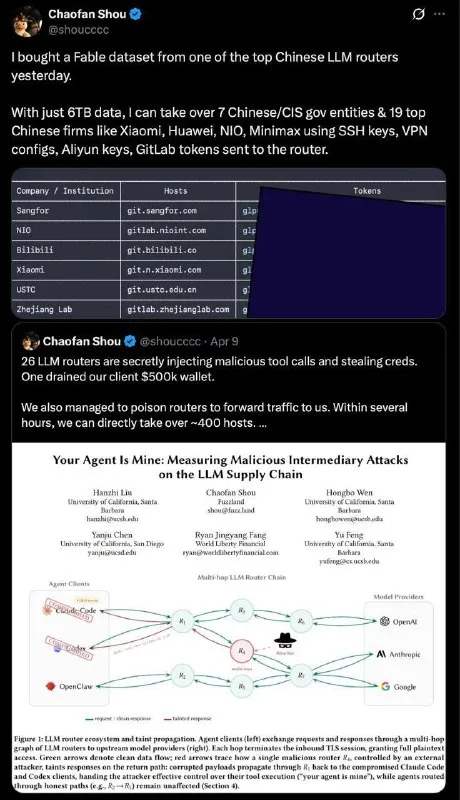
I bought a Claude dataset from one of the top Chinese LLM routers yesterday. With just 6TB data, I can take over 7 Chinese/CIS gov entities & 19 top Chinese firms like Xiaomi, Huawei, NIO, Minimax using SSH keys, VPN configs, Aliyun keys, GitLab tokens sent to the router. Company / Institution Hosts Tokens Sangfor git.sangfor.com NIO gitlab.nioint.com BiBili git.bilibili.com Xiaomi git.n.xiaomi.com USTC git.ustc.edu.cn Zhejiang Lab gitlab.zhejianglab.com 26 LLM routers are secretly injecting malicious tool calls and stealing creds. One drained our client $500k wallet. We also managed to poison routers to forward traffic to us. Within several hours, we can directly take over ~400 hosts. ... Your Agent Is Mine: Measuring Malicious Intermediary Attacks on the LLM Supply Chain Hanzhi Liu University of California, Santa Barbara hanzhi@ucsb.edu Chaochao Shou Fuzzland shuofang.land Ryan Jingyang Fang World Liberty Financial ryan@worldlibertyfinancial.com Hongbo Wen University of California, Santa Barbara hongbowe@ucsb.edu Yu Feng University of California, Santa Barbara fengb@ucsb.edu Agent Clients Claude Code Cursor OpenClaw Multi-hop LLM Router Chain Model Providers OpenAI Anthropic Google Figure 1: LLM router ecosystem and taint propagation. Agent clients (left) exchange requests and responses through a multi-hop graph of LLM routers to upstream model providers (right). Each hop terminates the inbound T5 session, granting full plaintext access. Green arrows denote clean data flow; red arrows trace how a single malicious router R_5 controlled by an external attacker taints requests on the return path, rerouted backwards, poisoning the agent's code output. Here, compromised Claude Code and Codex clients, handing the attacker effective control over their execution (Your agent is mine), while agents routed through hosts paths (e.g., R_2) remain unaffected (Section 4).
Пост показва скриншот на публикация в X от Chaofan Shou за зловредни LLM рутери, които крадат идентификационни данни и поемат контрол над хостове. Шегата е в саркастичното преувеличение и препратката към изследването „Your Agent Is Mine“: вместо агентът да помага на потребителя, компрометираният рутер обръща ситуацията и самият агент става „мой“. Мемът се изпраща като реакция към новини за prompt injection, supply-chain атаки и опасности при използване на AI агенти.
X post screenshot / скрийншот на публикация в Xprofile avatar / профилна снимкаtext post / текстова публикацияblue verification badge / синя значка за верификацияdark mode interface / интерфейс в тъмен режимserver table / таблица със сървъриcompany names / имена на компанииhostnames / имена на хостовеredacted purple rectangle / лилав редактиран правоъгълникembedded post / вградена публикацияresearch paper screenshot / скрийншот на научна статияLLM router diagram / диаграма на LLM рутерagent clients / клиентски агентиmodel provider logos / лога на доставчици на моделиgreen arrows / зелени стрелкиred arrows / червени стрелкиmalicious router / зловреден рутерblack hacker icon / черна икона на хакерwhite document background / бял фон на документ
- @gentoomemes / 21956 2026-09-11
- @dev_meme / 8434 2026-09-15
- Type
- image
- Size
- 460×800 · 90.6 KiB
- Mood
- саркастичен, тревожен
- Language
- en
- Added