Hacker Gets a Lifetime Membership
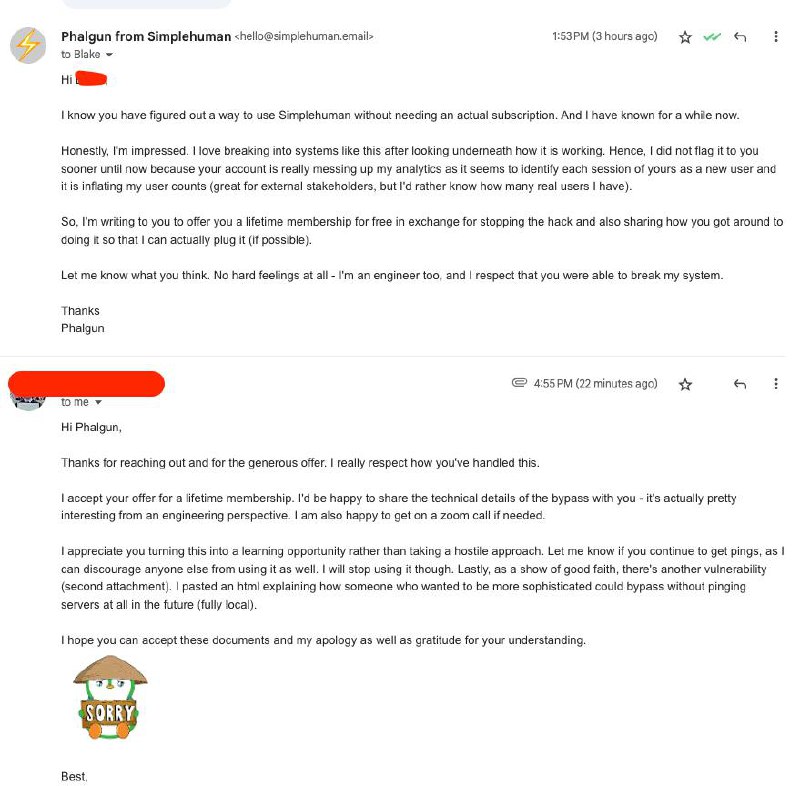
Phalgun from Simplehuman <hello@simplehuman.email> Hi [redacted] I know you have figured out a way to use Simplehuman without needing an actual subscription. And I have known for a while now. Honestly, I'm impressed. I love breaking into systems like this after looking underneath how it is working. Hence, I did not flag it to you sooner until now because your account is really messing up my analytics as it seems to identify each session of yours as a new user and is inflating my user counts (great for external stakeholders, but I'd rather know how many real users I have). So, I'm writing to you to offer you a lifetime membership for free in exchange for stopping the hack and also sharing how you got around to doing it so that I can actually plug it (if possible). Let me know what you think. No hard feelings at all - I'm an engineer too, and I respect that you were able to break my system. Thanks Phalgun [redacted] Hi Phalgun, Thanks for reaching out and for the generous offer. I really respect how you've handled this. I accept your offer for a lifetime membership. I'd be happy to share the technical details of the bypass with you - it's actually pretty interesting from an engineering perspective. I am also happy to get on a zoom call if needed. I appreciate you turning this into a learning opportunity rather than taking a hostile approach. Let me know if you continue to get pings, as I can discourage anyone else from using it as well. I will stop using it though. Lastly, as a show of good faith, there's another vulnerability (second attachment). I pasted an html explaining how someone who wanted to be more sophisticated could bypass without pinging servers at all in the future (fully local). I hope you can accept these documents and my apology as well as gratitude for your understanding. SORRY Best,
Скриншот переписки по электронной почте между разработчиком Simplehuman и пользователем, который обошёл платную подписку. Разработчик предлагает пожизненное членство в обмен на прекращение взлома и объяснение метода, а пользователь вежливо принимает предложение и тут же сообщает о новой уязвимости. Шутка строится на чрезмерно вежливом и конструктивном отношении хакера, который извиняется, делится ещё одним способом обхода и превращает взлом в дружеский инженерный обмен.
email interface / интерфейс электронной почтыemail conversation / переписка по электронной почтеlaptop or computer screen / экран ноутбука или компьютераredacted sender name / скрытое имя отправителяredacted recipient name / скрытое имя получателяemail address / адрес электронной почтыsubscription / подпискаlifetime membership offer / предложение пожизненного членстваhacker / хакерengineer / инженерtext paragraphs / текстовые абзацыreply message / ответное сообщениеattachment indicator / индикатор вложенияSORRY sticker / стикер «SORRY»green check marks / зелёные галочкиstar icons / значки звездыreply icons / значки ответаthree-dot menu / меню из трёх точек
- @dev_meme / 7194 2025-10-02
- Type
- image
- Size
- 800×786 · 102.4 KiB
- Mood
- absurdly polite
- Language
- en
- Added