Nasty Things That Might Happen
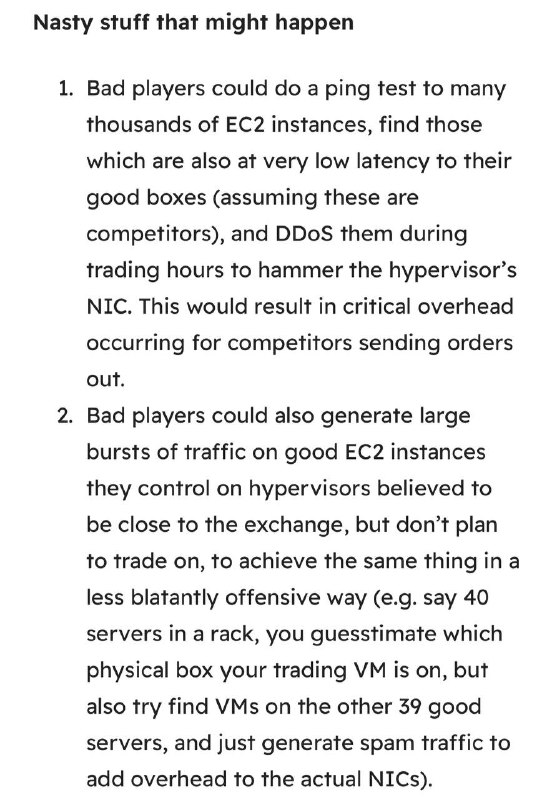
Nasty stuff that might happen 1. Bad players could do a ping test to many thousands of EC2 instances, find those which are also at very low latency to their good boxes (assuming these are competitors), and DDoS them during trading hours to hammer the hypervisor’s NIC. This would result in critical overhead occurring for competitors sending orders out. 2. Bad players could also generate large bursts of traffic on good EC2 instances they control on hypervisors believed to be close to the exchange, but don’t plan to trade on, to achieve the same thing in a less blatantly offensive way (e.g. say 40 servers in a rack, you guesstimate which physical box your trading VM is on, but also try find VMs on the other 39 good servers, and just generate spam traffic to add overhead to the actual NICs).
A screenshot presents a heading and two numbered examples of malicious network tactics targeting low-latency cloud trading infrastructure. The punchline is the bleakly practical list of ways bad actors could create latency and disrupt competitors, making it useful as a reaction to discussions about cloud-based exchanges and security risks.
document screenshot / скриншот документаtext block / текстовый блокnumbered list / нумерованный списокheading / заголовокparagraph / абзацblack text / чёрный текстwhite background / белый фонtechnical article excerpt / отрывок технической статьиnetwork attack / сетевую атакуcloud server / облачный серверcomputer infrastructure / компьютерную инфраструктуруtrading system / торговую систему
- @jemalloc / 1556 2024-04-16
- Type
- image
- Size
- 557×800 · 93.9 KiB
- Mood
- bleakly technical
- Language
- en
- Added